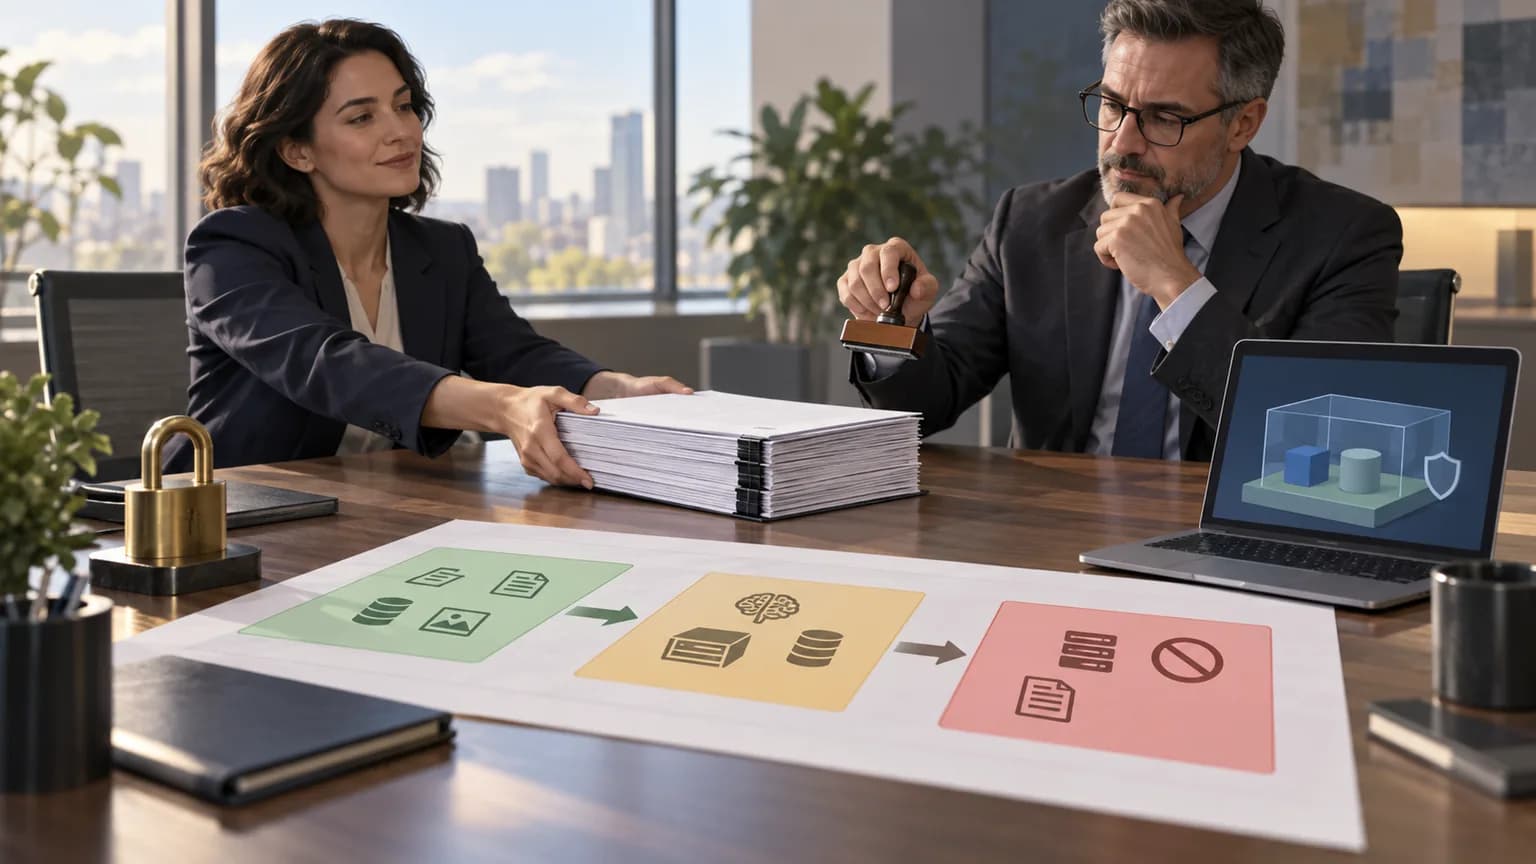
An LLM pilot is approved by information security when the team brings not an idea, but a package: which classes of data will go into the model, where the model is hosted, how the data is masked, who can see the request logs, which actions require human approval, and which isolated environment the testing takes place in. According to Content AI research, information security is named the main blocking factor by 76% of surveyed companies, and 83% say it is critical to start with a lightweight cloud pilot on non-sensitive data and measure the impact over 2–3 months. That means you should align with information security before the pilot starts, not after.
Prepared by AIrassvet October 15, 2026 based on Content AI’s study, “Pilot First, Strategy Second: How Large Businesses Are Implementing LLMs,” published on Habr on October 14, 2026 (more than 50 in-depth interviews with IT and information security leaders from mid-sized and large businesses). It is intended for CIOs, digital transformation leaders, and business process owners preparing their first pilot with a language model. We did not conduct our own survey: all percentages belong to Content AI, while the data matrix, information security package, and pilot plan are the editorial team’s methodology. This article is not legal advice: requirements related to personal data and trade secrets should be reviewed with your company’s legal and information security teams. AIrassvet is not affiliated with Content AI; the section at the end of the article describes the publisher’s services.
Contents
- At a Glance
- What the Content AI Study Showed
- Why Information Security Slows Down LLM Projects
- What Data You Can Use in a Pilot
- Where to Host the Model in the Pilot and in Production
- The Package for Information Security Approval
- A One-Quarter Pilot Plan
- How to Decide Whether to Scale the Pilot
- Common Mistakes
- Frequently Asked Questions
- Primary Sources and Verification Method
At a Glance
- Use cases emerge faster than strategies. Generative AI is already operating in business processes at 53% of the companies surveyed by Content AI; another 29% are running pilots, and half do not have an approved AI strategy.
- Information security is the main barrier. 76% of respondents named it the blocking factor; only 6% pointed to economics and ROI.
- The decision depends on the data class. For personal data, 62% of companies in one form or another block transfer to external services; for trade secrets, only 19% are willing to give them to an external model.
- Start with a lightweight pilot, not a cluster. High CAPEX significantly slows pilots for 77% of respondents; 83% want to start in the cloud with non-sensitive data and move the solution to an internal environment after success.
- Approval is accelerated by a document package: data map, model hosting, masking, logging, human approval, test environment, and accountability model.
What the Content AI Study Showed
Content AI conducted more than 50 in-depth interviews with IT and information security representatives from companies in retail, banking, oil and gas, power, telecom, and other industries (Habr, 10/14/2026). This is a qualitative study with a small sample, so the percentages should be read as a snapshot of large business sentiment, not as statistics for the entire market.
| Metric | Share of respondents |
|---|---|
| Generative AI in operational processes | 53% |
| Running pilot projects | 29% |
| Employees using models only for personal tasks | 18% |
| Consider themselves at “level 2”: evaluating pilot results, not yet in production | 41% |
| Believe they have reached “level 4–5”: hybrid models, policies, measurable impact | 6% |
| Ready to pilot fully autonomous agents | 15% |
The paradox the authors note is that implementation use cases are appearing faster than AI strategies. The typical picture: there is an AI item in the overall digitalization strategy, but no specific provisions on data, model selection, or agent use. Hence the study’s title: pilot first, strategy second.
For how to measure the gap between access to a model and real-world processes, see our article on the AI implementation gap in companies.
Why Information Security Slows Down LLM Projects
According to Content AI, the initiative for an LLM project comes from multiple departments at once in 47% of companies, from the business side in 27%, and from IT and top management in 26%. But one department most often stops projects:
| LLM Project Blocking Factor | Share of respondents |
|---|---|
| Information security department | 76% |
| Economics and ROI | 6% |
| Bureaucracy and procurement | 6% |
| Combination of factors | 12% |
It is important to understand information security’s logic: it is responsible for risk, not for results. A language model is a new channel through which data can leave the perimeter, and an agent is a new actor with permissions in corporate systems. Until the company has a policy, information security is forced to assess each project from scratch: according to the study, 53% of companies make decisions on a case-by-case basis, and only 47% have preapproved policies.
A ban without a safe alternative does not work either. Experts in the study note that a total ban creates “shadow AI”: employees use public services secretly. 56% of respondents consider a corporate gateway through which all external LLM requests pass, with logging and filtering, the most successful strategy; another 22% try to block employees and admit that it does not work. For more on how to find and legalize such connections, see our article on shadow AI.
What Data You Can Use in a Pilot
Willingness to share data externally among the companies surveyed depends on the information class (Content AI):
| Data class | What companies say | Practical takeaway for the pilot |
|---|---|---|
| Personal data | 31% — absolutely no transfer, 31% — only within their own environment, 38% — external model is acceptable with masking and a separate agreement | Pilot without personal data or with masking; for production, use your own environment |
| Trade secrets and know-how | 56% — only within their own environment, 25% — a complete ban on LLM processing, 19% — are ready to hand data over to an external model | Do not use in a cloud pilot |
| Service desk, tickets, open data | 46% are ready to run it in the cloud, 38% — conditionally | A good candidate for a first pilot |
| Financial and payment transactions by an agent | 80% — only with mandatory human approval | The agent prepares the transaction, and a human approves it |
The study also separately notes industry-specific bans: in the banking sector, the use of public cloud models and services built on them is fully prohibited.
Respondents consider data masking the strongest protection measure: 91% acknowledged that it can remove some internal restrictions and open the door to hybrid setups. But some experts warn that masking alone will not help if the data still travels over an unsecured channel. We covered how anonymization works before sending data to a model in the article on sending customer data to AI.
For personal data of Russian citizens, there is also a direct legal requirement: when collecting personal data, recording, systematization, accumulation, storage, clarification, and retrieval using databases outside Russia are not permitted, except in cases specified by law (Federal Law No. 152-FZ, Article 18, Part 5). What this means for foreign AI services is covered in the article on 152-FZ and foreign AI.
Where to host the model in a pilot and in production
For the main platform, respondents to Content AI choose as follows: in-house infrastructure — 41%, hybrid setup — 35%, cloud services — 24%. No one selected the “private cloud” option: in practice, it is treated as cloud, and information security teams view it with skepticism.
The picture is different in pilots: 65% of respondents allow a launch in a public cloud using non-sensitive or synthetic data, 21% allow it with real data, and 14% are against the cloud even for pilots. Attitudes toward models also vary:
- foreign APIs: 37% of companies have a direct internal ban, 50% allow limited use, and 13% use them under contract;
- Russian cloud LLMs: 70% consider the quality insufficient, 30% use them or are ready to use them;
- Chinese and open models in a closed environment: 56% view them positively or already use them, 25% are cautious, and 19% are neutral.
The key takeaway from the study: the model’s origin has not yet become the decisive factor; what matters more is how data control is implemented. That is why 86% of respondents value or want the ability to bring their own model (BYO-LLM), and 56% need turnkey infrastructure support.
Why you should not start by buying a cluster. High CAPEX is a major obstacle to pilots for 77% of respondents. The authors describe a typical scenario: the vendor promises a fast return on investment, but first suggests buying a compute cluster for 20–30 million rubles, which is nearly impossible with shrinking IT budgets. 83% believe it is critical to start with a lightweight cloud pilot, measure the impact over 2–3 months, and only move the solution into the internal environment if it succeeds. A comparison of cloud and on-premises environments by total cost is in the article on cloud vs. on-prem LLMs.
Approval package for information security
The study identifies three elements used to overcome the infosec barrier: a document package, a test environment, and a clear responsibility model. Below is the composition of such a package in the AIrassvet editorial team’s version. This is a preparation checklist, not a regulatory list.
- Scenario description. One process, the pilot users, what the model does and does not do, the expected impact, and the metric.
- Data map. Which data classes go into prompts, the knowledge base, and logs; the source of each class; whether there is personal data or trade secret information.
- Hosting and model. Cloud, hybrid, or in-house environment; specific model and provider; processing jurisdiction; data retention terms with the provider.
- Data protection measures. Masking before sending, an enterprise gateway to models, prompt and response filtering, encrypted channels.
- Access rights and actions. Which systems the model or agent is connected to, read-only or write access, which actions require human approval.
- Logging. What is written to the log, where it is stored, who has access, how long it is retained — the prompt log itself contains sensitive data.
- Test environment. An isolated sandbox, synthetic or anonymized data, pilot duration, stop conditions.
- Responsibility model. Process owner, data owner, model owner, incident response procedure.
If a company has many AI services, item 4 is best handled through a single gateway with filtering and logging — that way, infosec approves not each application, but one control point.
One-quarter pilot plan
The 2–3 month horizon comes from Content AI respondents’ expectations; the phase breakdown is the editorial team’s methodology, not the result of our project.
| Stage | What to do | Result for infosec and the business |
|---|---|---|
| Preparation | Choose a process with non-sensitive data, establish a baseline metric, and assemble the package for infosec | An approved package and a measured baseline |
| Launch in the sandbox | Connect the model through the gateway, enable logging, and apply masking if needed | A working prototype in the test environment |
| User testing | A small group of employees uses the solution on real tasks | Data on impact, errors, and incidents |
| Evaluation | Compare the metric with the baseline, and review logs and incidents together with infosec | Decision: stop, improve, or scale |
We described how to fit the first version of an AI solution into a short timeframe in the article on an AI MVPand how to choose a process and establish a baseline in the material on auditing business processes.
How to decide whether to scale a pilot
The study emphasizes that mid-sized businesses want to see results within a quarter, while large enterprises are willing to calculate total cost of ownership over several years, but without a quick proof of results, they do not allocate large budgets. Before deciding to scale, you should answer the following questions:
- Was the impact criterion set before launch achieved?
- Were there any data incidents, and how were they resolved?
- Which data classes will be needed during scaling, and do they require moving to your own environment?
- How much will production cost when you factor in infrastructure, not just the pilot?
- Who will own the solution after the pilot?
Why moving it into your own environment matters. A pilot on non-sensitive data proves the impact, but production almost always involves more sensitive information. That’s why you should build in an architecture that lets you swap the model and bring it in-house right from the pilot stage.
Common mistakes
- Going to information security with an idea instead of a complete package. Without a data map, security will assess the worst-case scenario.
- Using personal data or trade secrets in the first pilot. That moves the pilot into the category of projects that most surveyed companies allow only within their own environment.
- Starting with hardware purchases. The study’s authors associate investment in a private environment with a live production setting, not with a pilot.
- Giving the agent full autonomy. Only 15% of companies are ready to pilot fully autonomous agents; 38% support agents only with human involvement.
- Not setting a baseline metric. Without a starting point, you can’t prove impact within a quarter.
Common questions
Why does the security team block LLM projects?
A language model is a new channel through which data can leave the perimeter, and an agent is a new entity with permissions in corporate systems. Until the company has an AI policy, security evaluates each project from scratch and sees the worst-case scenario. According to Content AI research, security is the main blocking factor for 76% of respondents.
Can you run an LLM pilot in the cloud?
Yes, if no sensitive data is involved in the pilot. According to Content AI, 65% of respondents allow a launch in a public cloud using non-sensitive or synthetic data, while only 21% allow it with real data. Personal data and trade secrets are better left out of a cloud pilot.
What documents are needed to get an AI pilot approved by security?
A scenario description, a data map by class, a deployment and model choice, data protection measures, the model’s or agent’s permissions in systems, logging rules, a description of the test environment, and an accountability model. This package allows security to assess specific risks instead of hypothetical ones.
Does data masking help get approval?
Often yes: 91% of Content AI respondents believe masking can remove some restrictions and open the door to hybrid setups. But masking does not replace a secure channel, access control for logs, or legal requirements for personal data.
How long should an LLM pilot last?
Content AI respondents expect 2–3 months to measure impact; middle-market companies want to see results within a quarter. The timeline should be fixed in advance together with the metric and stop conditions.
Do you need an AI strategy before the first pilot?
Not necessarily: half of the surveyed companies don’t have one, yet use cases are already working. But basic rules—what data can be shared, which models are allowed, and who is responsible for the solution—should be agreed on before launch, otherwise every new project will go through approval again.
Original sources and verification method
Method: On October 15, 2026, we read the full Content AI study, extracted all percentages along with the wording of the questions, and cross-checked the requirement for local storage of personal data against the text of Federal Law No. 152-FZ. AIrassvet did not conduct its own survey; the data matrix, security package, pilot plan, and decision checklist are the editorial team’s methodology.
- Habr, 10/14/2026: Content AI, “Pilot First, Strategy Later: How Large Enterprises Implement LLMs” — all percentages in the article.
- Federal Law No. 152-FZ “On Personal Data”: Article 18, Part 5 — localization of databases containing personal data of Russian citizens.
Limitations: the Content AI sample included more than 50 interviews with mid-sized and large businesses, with no breakdown by industry disclosed; the method used to calculate the percentages is not described in detail in the publication. The study was published in Content AI’s corporate blog, not in an independent outlet, which should be kept in mind when reading the conclusions.
How AIrassvet helps prepare an LLM pilot
A pilot gets through security faster when the process, data, and architecture are described before the first meeting with the security team. On the AIrassvet website the following areas are described as directly relevant to this task:
- process audit and data preparation: selecting a process for the pilot, the baseline metric, and a map of data classes;
- deployment of language models on the client’s servers — when the solution needs to be moved into an internal environment after the pilot;
- MVP development, integration, and testing in an isolated environment before real users are connected;
- team training on using the solution after launch.
The first step is to choose one process, document its current metric, describe the data sources and security constraints, and agree on what result will count as a successful pilot.
Bottom line: align with security before launch
The Content AI study shows that the debate over the value of LLMs for large enterprises is over, and the main barrier is not economics but information security. Companies want a lightweight pilot with limited investment and a clear quarterly impact, but that kind of pilot is only possible if security knows in advance what data will go where.
So start with a process using non-sensitive data, come to security with a document package, build in a test environment and an accountability model, and design the architecture so you can move the solution into your own environment after a successful pilot.